Incident Readiness
Being prepared for a cyber incident starts before the incident occurs.
A cyber incident within an OT environment often has a direct impact on operational processes. Production lines can come to a standstill, systems can become unavailable, or critical processes can no longer be controlled safely. That is precisely why preparedness is essential.
Many organizations invest in preventive security measures but have not fully defined what actually needs to be done when an incident occurs. Who makes the decisions? Which systems take priority? How is escalation handled? And how is a secure recovery carried out without further jeopardizing business continuity?
OTconnect helps organizations prepare for cyber incidents in industrial environments.
Be Prepared for the Unexpected
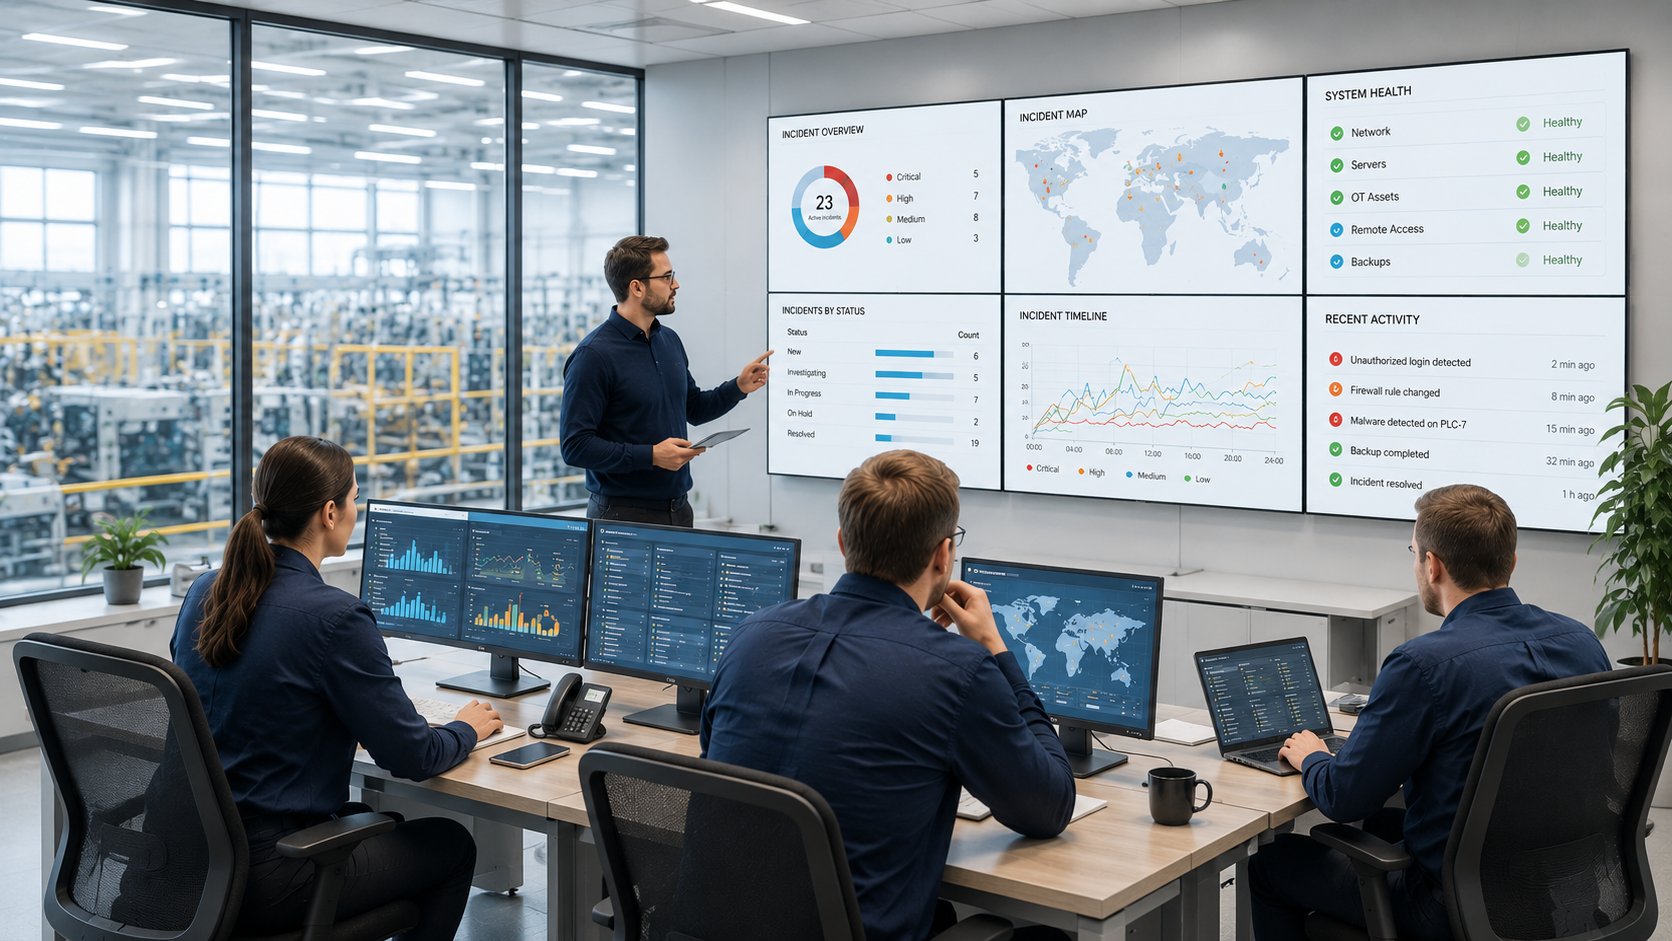
Incident Readiness is about creating structure, clarity, and clear agreements before an incident occurs. The goal is not only to improve cybersecurity, but above all to minimize the impact on operational processes when a disruption occurs.
In doing so, we focus specifically on the characteristics of OT environments, where availability, security, and continuity are often more important than traditional IT priorities.
Together with the organization, we will, among other things, identify:
OT Calls for a Different Approach
A cyber incident in OT differs fundamentally from an incident in an office environment. Industrial systems may rely on legacy equipment, specific vendors, or processes that cannot simply be shut down.
That is why OT Incident Readiness requires a practical and realistic approach, tailored to the operational environment.
OTconnect supports organizations in the following areas, among others:
From Theory to Practical Feasibility
Documentation alone is not enough. Procedures must be practical and applicable in the organization’s day-to-day operations.
That is why we focus on practical applicability. Together, we assess whether existing processes are actually feasible during an incident and where improvements are needed.
By reviewing scenarios and potential disruptions, we gain a better understanding of:
This helps organizations respond more quickly, in a more controlled manner, and with less impact when a disruption actually occurs.
Compliance and Governance Support
Regulations such as NIS2 and standards such as IEC 62443 place an increasing emphasis on demonstrable preparedness, risk management, and organizational measures.
Incident Readiness helps organizations to:
This not only enhances resilience but also provides greater administrative control over cyber risks within the OT environment.
Resilience starts with preparation
There is no such thing as complete prevention of incidents. However, organizations can significantly limit the impact of disruptions by planning ahead for processes, responsibilities, and recovery.
OTconnect helps organizations not only to better secure their OT environments, but also to be better prepared for situations in which security measures fall short.
That is the foundation of true cyber resilience.